Kubernetes Installation
You can use Kubernetes to install Litmus Edge.
Before you begin
- Get access to a configured Kubernetes cluster.
- Get access to PersistentVolumeClaim (PVC). Learn more about Persistent Volumes from the Kubernetes documentation.
- Get administrative permissions to run the kubectl command-line tool.
- Contact your Litmus account representative to get access to the service account .json file.
- Depending on the specific requirements of your environment, you may need to get access to a storage class. Learn more about Storage Classes from the Kubernetes documentation.
To use Kubernetes to install Litmus Edge, you will need to do the following:
- Step 1: Launch a Litmus Edge Kubernetes
- Step 2: Log in to Litmus Edge
Step 1: Launch a Litmus Edge Kubernetes
To launch a Litmus Edge using Kubernetes:
1. Download the service account .json file, which you can get from your Litmus account representative. 2. Open a Command Prompt Terminal (CTRL+R). 3. Execute the following commands to setup credentials for a Kubernetes namespace.
kubectl create namespace le-prodThe command creates a namespace named le-prod.
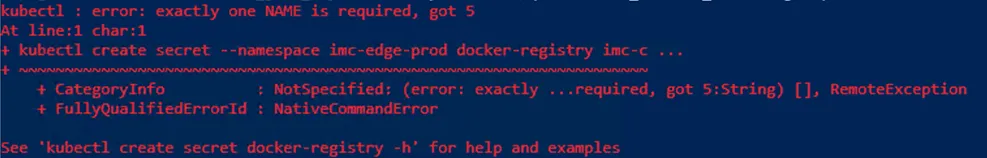
kubectl create secret --namespace le-prod docker-registry litmus-credential --docker-server=us-docker.pkg.dev --docker-username=_json_key --docker-password="$(cat ~/<file_name>.json)"Important: If you encounter an error as shown in the screenshot below when using Windows PowerShell, make sure to follow these steps:
- The namespace has been created
- There are no spaces in the command
- Replace the double quotes with single quotes
Refer to the command parameters:
- kubectl create secret sets a Secret for use with a Docker registry.
- --namespace le-prod sets up a Kubernetes namespace of le-prod.
- docker-registry litmus-credential sets up Secret name as litmus-credential. This should not be changed.
- --docker-server=us-docker.pkg.dev sets the Docker registry server as us-docker.pkg.dev. This should not be changed.
- --docker-username=_json_key sets the Docker registry username to connect to the server above. This should not be changed.
- --docker-password="$(cat ~/<file_name>.json)" retrieves the password within the service account file requested from step 1.
- --docker-password="$encodedPassword" retrieves the password within the service account file requested from step 1 (Powershell).
Note: le-prod should be changed to an isolated namespace to suit deployment best.
4. Copy or download the following Litmus Edge deployment file.
# Create ServiceAccount
apiVersion: v1
kind: ServiceAccount
metadata:
  name: litmusedge-docker
  namespace: le-prod
  labels:
    app.kubernetes.io/name: litmusedge-docker
    app.kubernetes.io/instance: litmusedge-instance
---
# Create PVC
kind: PersistentVolumeClaim
apiVersion: v1
metadata:
  name: litmusedge-data
  namespace: le-prod
  labels:
    app.kubernetes.io/name: litmusedge-docker
    app.kubernetes.io/instance: litmusedge-instance
spec:
  accessModes:
    - "ReadWriteOnce"
  resources:
    requests:
      storage: "10G"
---
# Create Service
apiVersion: v1
kind: Service
metadata:
  name: litmusedge-docker
  namespace: le-prod
  labels:
    app.kubernetes.io/name: litmusedge-docker
    app.kubernetes.io/instance: litmusedge-instance
spec:
  type: ClusterIP
  ports:
    - port: 443
      targetPort: https
      protocol: TCP
      name: https
  selector:
    app.kubernetes.io/name: litmusedge-docker
    app.kubernetes.io/instance: litmusedge-instance
---
# Create Deployment
apiVersion: apps/v1
kind: Deployment
metadata:
  name: litmusedge-docker
  namespace: le-prod
  labels:
    app.kubernetes.io/name: litmusedge-docker
    app.kubernetes.io/instance: litmusedge-instance
spec:
  replicas: 1
  selector:
    matchLabels:
      app.kubernetes.io/name: litmusedge-docker
      app.kubernetes.io/instance: litmusedge-instance
  template:
    metadata:
      labels:
        app.kubernetes.io/name: litmusedge-docker
        app.kubernetes.io/instance: litmusedge-instance
    spec:
      serviceAccountName: litmusedge-docker
      securityContext:
        {}
      imagePullSecrets:
        - name: litmus-credential
      containers:
        - name: litmusedge-docker
          securityContext:
            capabilities:
              add:
              - NET_ADMIN
          image: "us-docker.pkg.dev/litmus-sales-enablement/litmusedge/litmusedge-std-docker:latest"
          imagePullPolicy: IfNotPresent
          ports:
            - name: https
              containerPort: 443
              protocol: TCP
          volumeMounts:
            - mountPath: /var
              mountPropagation:
              name: litmusedge-data
              subPath:
              subPathExpr:
          resources:
            requests:
              cpu: 1
              memory: 1024Mi
            limits:
              cpu: 4
              memory: 4096Mi
      volumes:
        - name: litmusedge-data
          persistentVolumeClaim:
            claimName: litmusedge-data
5. Execute the following command to deploy a Litmus Edge Kubernetes cluster using the deployment file from Step 4.
kubectl apply -f litmusedge-deployment.yaml --namespace le-prodRefer to the command parameters:
- -f litmusedge-deployment.yaml uses the file litmusedge-deployment.yaml for deployment. This should not be changed.
- --namespace le-prod sets le-prod to be the deployment that Kubernetes will use.
Special and Additional Considerations:
- Litmus Edge can function in both single and multi Kubernetes node clusters, and can support various networking modes. Your Kubernetes admin has the responsibility to configure proper networking.
- Adjust CPU/RAM/Storage for the Kubernetes cluster as needed. Storage should be set to at least 10GB. Scale additional computing resources when using Litmus Edge features that require high-computing power, such as PLC drivers, integrations, and Flows.
- Ensure credentials are stored properly with Kubernetes management.
- NET_ADMIN permissions are required.
Step 2: Log in to Litmus Edge
- See Access the Terminal User Interface for instructions on how to navigate and log in for the first time.
Note: To identify the port configured by the admin, use the following command: kubectl get svc -n le-prod